

Enterprise DDoS Attack Protection.
Keep your business online when attacks hit.
vXtream DDoS Mitigation
DDoS protection is built into the vXtream network, helping keep your online services available when malicious traffic attempts to overwhelm them. All Elastic Compute customers receive standard DDoS protection as part of their service.
For organisations requiring additional protection, our managed enterprise-level DDoS Mitigation service provides enhanced protection with pricing based on the volume of clean-return traffic.
Standard DDoS Protection
Protection built into the network.
Our network is protected against DDoS attacks, with standard DDoS protection included for all Elastic Compute customers. Enterprise-level DDoS Mitigation is also available for customers requiring additional protection.
On-Demand DDoS Mitigation
Always-On Enterprise DDoS Mitigation
Continuous protection. No waiting.
Traffic is continuously monitored and malicious traffic identified and mitigated before it reaches your network, helping keep critical services available around the clock.
What is a DDoS Attack?
A Distributed Denial of Service (DDoS) attack attempts to make a website, application or online service unavailable by overwhelming it with malicious traffic from multiple sources.
DDoS attacks can target any organisation with an online presence, disrupting critical services, affecting customers and damaging business operations. The challenge is identifying and filtering malicious traffic quickly enough to keep legitimate users connected.
When staying online matters.

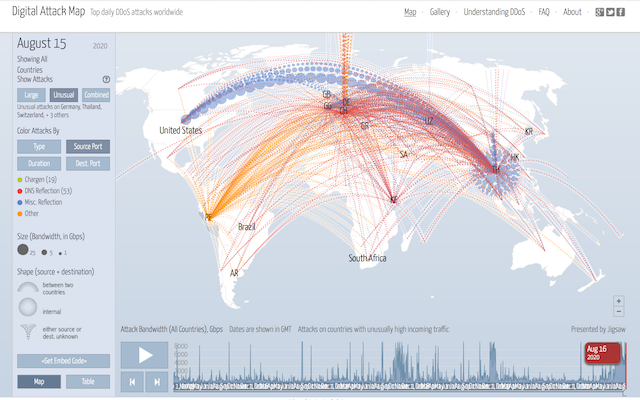
Your website and online services are critical to your business. A successful DDoS attack can overwhelm your infrastructure with malicious traffic, disrupting services, affecting customers and quickly turning availability into a business-critical issue.
DDoS attacks are becoming larger, more frequent and more sophisticated, but the objective remains the same: keep legitimate users from accessing your services. Effective mitigation means detecting the attack quickly, filtering malicious traffic and keeping your business online.
Types of Attacks
DDoS attacks come in different forms, but they all have the same objective: overwhelm a network, system or application and prevent legitimate users from accessing a service.
Attack Class: Four common categories of attacks
TCP Connection Attacks - Exhausting connections
Attempt to consume the available connections on firewalls, load balancers and application servers, potentially preventing legitimate traffic from getting through.
Fragmentation Attacks - Overloading packet processing
Flood systems with fragmented TCP or UDP packets, consuming resources as they attempt to reassemble the traffic and degrading performance.
Application Attacks - Targeting specific services
Target a particular application or service rather than simply overwhelming the network. These attacks can be effective with relatively small amounts of traffic, making them harder to detect.
Volumetric Attacks - Consuming bandwidth
Flood the target network or service with enormous volumes of traffic, creating congestion and preventing legitimate users from accessing the service.
Amplification attacks – some DDoS attacks use legitimate network services to multiply the volume of traffic directed at a target
DNS Reflection - Amplifying traffic through DNS
Attackers send requests to DNS servers using a spoofed source address, causing much larger responses to be directed towards the victim
Chargen Reflection - Exploiting legacy services
The outdated Chargen protocol can generate streams of response traffic and has historically been abused to amplify DDoS attacks.
vXtream Enterprise DDoS Mitigation Key Features
Protect Any Connection
Carrier-agnostic protection can re-route and scrub traffic from vXtream or third-party connections, supporting IPv4 and IPv6 with IP VPN Direct and GRE clean-traffic return options.
85+ Tbps of Protection Capacity
With 15 global scrubbing centres and more than 85 Tbps of FlowSpec-based defence capacity, vXtream can absorb and filter even large-scale DDoS attacks.
24/7 Monitoring & Support
Mitigation in Up to 10 Minutes
Up to 10-minute time-to-mitigate SLAs for most attacks once traffic reaches our scrubbing infrastructure.
Rapid Threat Defence
Global Scrubbing Network
Traffic is routed to the closest available scrubbing centre, with access to hundreds of partner internet and IP VPN points of presence worldwide.