


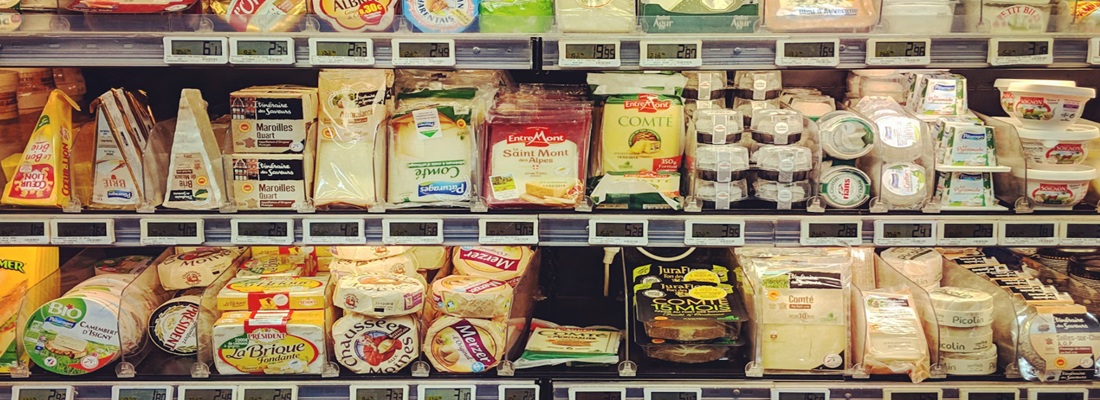
From hacked supermarket fridges and freezers to casino fish tanks, connected devices have been creating security headaches for years. So why are we still getting the basics wrong?
It sounds like the plot of a rather peculiar disaster movie. Supermarket fridges and freezers across France are hacked, their temperatures climb to extraordinary levels, and food that should be kept frozen begins to thaw, spoil and, in some cases, literally cook. The result is wasted stock, disrupted businesses and losses that could run into tens of millions of euros.
But this is no Hollywood fantasy. In October 2026, cyberattacks targeted refrigeration control systems at hundreds of French supermarkets. The incident demonstrated, rather spectacularly, that a cyberattack doesn’t have to steal customer records, encrypt business-critical files or bring a corporate network to its knees to cause serious damage.
Sometimes, it just needs to turn off the cold.
And perhaps the most uncomfortable question is this: after more than two decades of progress in cyber security, why are we still leaving such basic vulnerabilities exposed?
We’ve been here before
Cast your mind back to the early 2000s. As broadband became more widely available, businesses were connecting more systems to the internet, and security was beginning to move beyond the traditional perimeter defences of firewalls, patching, filtering and antivirus software.
Over the following years, the focus broadened towards endpoint protection and understanding what was actually happening on individual devices. Behavioural monitoring helped identify suspicious activity, while the emergence of Endpoint Detection and Response (EDR) brought much greater visibility into endpoint activity, helping security teams investigate incidents and respond to threats.
Security was evolving from simply trying to keep the bad guys out towards recognising when something had gone wrong, understanding what had happened and responding accordingly.
Around the same time, another idea was gathering momentum: the Internet of Things, and its broader cousin, the Internet of Everything. Popularised by Cisco around 2013, the latter described a connected world in which people, processes, data and things worked together.
It was an enticing vision. Sensors could monitor equipment remotely, connected devices could report faults before they became expensive failures, and businesses could use real-time data to improve efficiency and reduce costs.
And all of that remains true. The problem is that connectivity brings risk along with the benefits.
From fish tanks to freezers
We didn’t need the French supermarket attacks to discover that seemingly innocuous devices could become a security liability.
In 2017, Forbes reported that attackers had exploited an internet-connected fish tank thermometer in a casino to gain a foothold in its network and extract data. A fish tank might seem an unlikely starting point for a cyberattack, but its importance was not the aquarium itself. It was the connection.
More recently, concerns have been raised about the security of electric vehicle charging infrastructure, building management systems and other operational technology. Even digital road signs have been hijacked, demonstrating how connected systems can be manipulated to display messages their owners never intended.
The common thread is that devices designed to perform a particular function can also become entry points, targets or tools for disruption.
The French refrigeration attacks bring that risk into sharp focus. Reporting indicates that affected systems included older refrigeration controllers running outdated firmware, with some apparently retaining default passwords. Manufacturers had previously issued security advice and recommended updates or replacement of obsolete equipment. The precise methods used in the attacks, and the identity and motivation of those responsible, remain matters for investigation.
But the wider lesson is already clear. Systems that control physical equipment are part of the cyber security picture, whether or not the organisation operating them thinks of them as IT.
Has security lost sight of the basics?
It would be unfair to suggest that cyber security has stood still. Today’s organisations have access to far more sophisticated tools for endpoint protection, threat detection, monitoring and incident response than they did twenty years ago.
Yet technology alone cannot compensate for equipment that is no longer supported, software that hasn’t been updated, exposed management interfaces or credentials that have never been changed.
Nor does installing a security product automatically mean a device is secure. It needs to be configured properly, monitored, maintained and included in the organisation’s wider security arrangements.
The challenge is that the definition of an endpoint has expanded enormously. It no longer means just a laptop, desktop or server. It can mean a refrigeration controller, a charging station, a sensor or a remotely managed industrial device.
Some of these systems have long operational lives. They may have been installed by specialist contractors, use proprietary software and operate with little involvement from the organisation’s central IT team. Replacing them can be expensive, and taking them offline for maintenance may be difficult.
That creates an uncomfortable mismatch. The technology remains essential to the business, but responsibility for its security may be less clear than it should be.
The weakest link may belong to somebody else
There is another important dimension to the French incident: the supply chain.
A supermarket may own its stores and the stock inside them, but it may rely on external specialists to install and maintain refrigeration equipment. The equipment manufacturer supplies the controllers, while software and remote management services enable monitoring and adjustments from elsewhere.
That arrangement makes commercial sense. It allows businesses to draw on specialist expertise without having to manage every technical detail themselves.
But where does responsibility for cyber security sit?
A retailer may assume its refrigeration contractor is keeping systems secure. The contractor may depend on the equipment manufacturer’s updates and software. The manufacturer may advise customers to upgrade, but have no direct control over whether obsolete equipment is replaced or properly protected.
Every party may be doing some of the work, yet gaps can remain between them.
It is important not to jump to conclusions about the precise entry point in the French attacks. The available reporting does not establish that a compromised third-party app was responsible. However, the incident highlights a broader risk that applies well beyond refrigeration: an organisation’s security depends partly on the systems, suppliers and access arrangements it relies upon.
The same principle applies to cloud services, outsourced IT, remote maintenance and software supplied by third parties. Your own defences may be robust, but you still need to understand what access others have, what they are responsible for and how their security is assessed.
What should businesses be doing?
The answer isn’t to disconnect everything and retreat to a world before the internet. Connectivity delivers too many benefits for that to be realistic, and many businesses depend on connected systems to operate efficiently.
Instead, organisations need to understand what they have connected, why it is connected and what could happen if it were compromised.
That starts with maintaining an accurate inventory of devices and systems, including operational technology that may sit outside the traditional IT estate. Businesses should establish who owns each system, who maintains it, whether it is still supported and how its security is managed.
Default credentials must be changed, firmware and software kept up to date, and unnecessary internet exposure removed. Where possible, operational technology should be segmented from corporate IT so that a compromise in one area cannot automatically spread into another. Remote access should be tightly controlled, and monitoring should be capable of identifying unusual activity.
Crucially, businesses need to agree clear responsibilities with suppliers and contractors. That means understanding how remote access works, how vulnerabilities are reported and fixed, what happens when equipment reaches the end of its supported life, and who is accountable for making sure the necessary controls are in place.
And because prevention is never guaranteed, resilience matters too. Organisations should consider how they would continue operating if a connected system were taken offline, manipulated or rendered unusable. Back-up processes, contingency plans and tested incident response arrangements are as relevant to physical operations as they are to data and applications.
The next cyber incident may not look like a cyber incident
At vXtream, we have spent more than twenty years working with businesses as their infrastructure and security needs have evolved. The technology has changed enormously, but the underlying principle remains the same: security needs to be considered as part of the whole environment, not bolted on to individual components and assumed to take care of everything.
The French supermarket attacks are a timely reminder that cyber security is no longer simply about protecting servers, networks and data. It is also about protecting the physical operations that depend on connected technology, and understanding the risks introduced by suppliers, contractors and systems beyond the traditional corporate perimeter.
The fish tank was a warning. The fridges are another.
So here’s a question worth asking in your next security review: do you know what is connected to your business, who can access it, and what would happen if someone took control?
If the answer isn’t clear, it may be time to take a closer look.
At vXtream, we’re always happy to talk through your infrastructure and security concerns and help you work out where the risks may lie.
Image: Cheese fridge in French Supermarket by Alana Harris, Unsplash